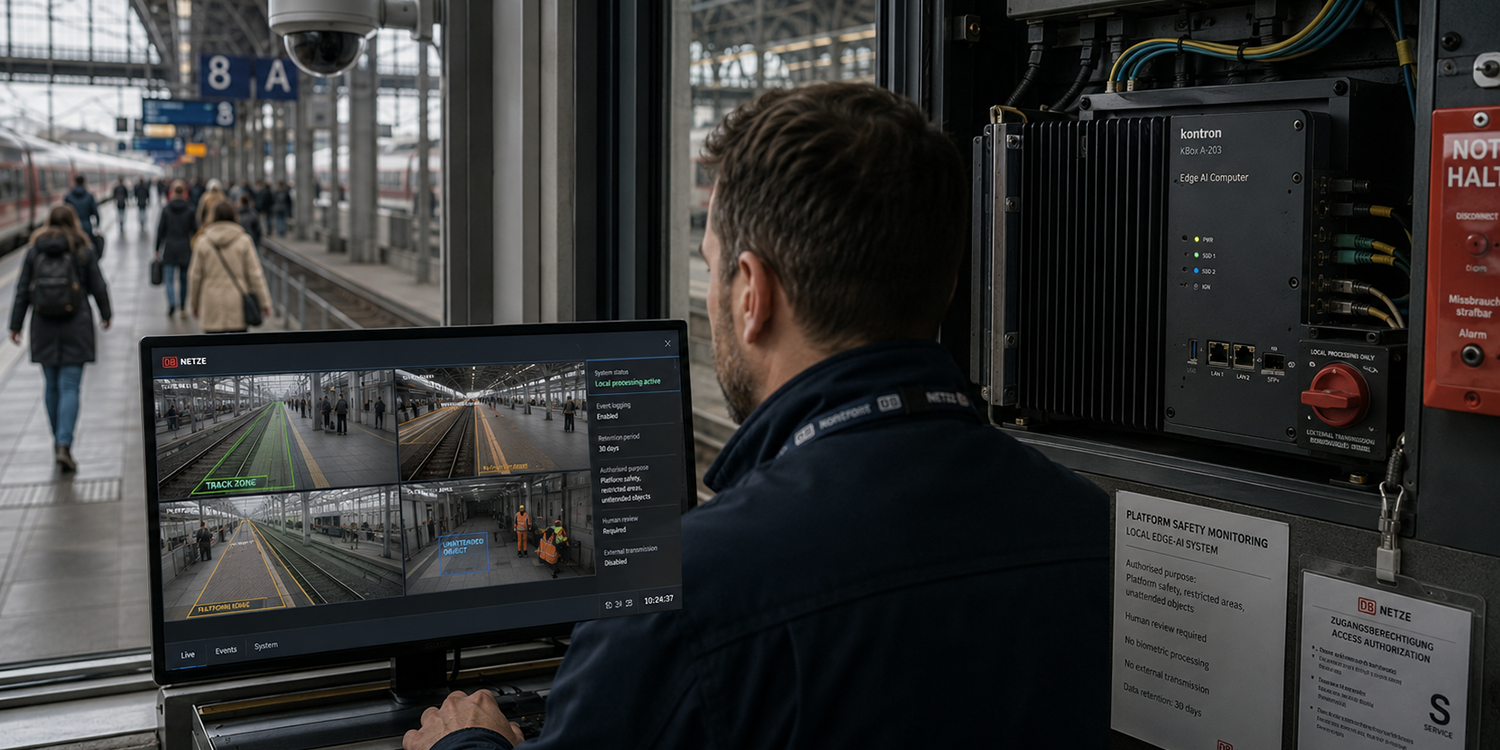
Edge intelligence is moving AI from distant cloud systems into everyday devices: factory sensors, medical equipment, vehicles, cameras, phones, and connected infrastructure. The EU AI Act is shaping that shift by making safety, transparency, oversight, and accountability part of the design conversation from the start. For teams building or buying AI-enabled devices, the message is simple: smarter devices also need smarter ai governance.
The EU AI Act means edge intelligence can no longer be treated as “just a device feature” when it affects people’s safety, rights, access to services, or public trust. The Act uses a risk-based approach, so the stricter duties apply where AI could cause greater harm, while many low-risk uses face little or no extra regulation. It entered into force on 1 August 2024 and became generally applicable on 2 August 2026, with staged deadlines for areas such as general-purpose AI and high-risk systems.
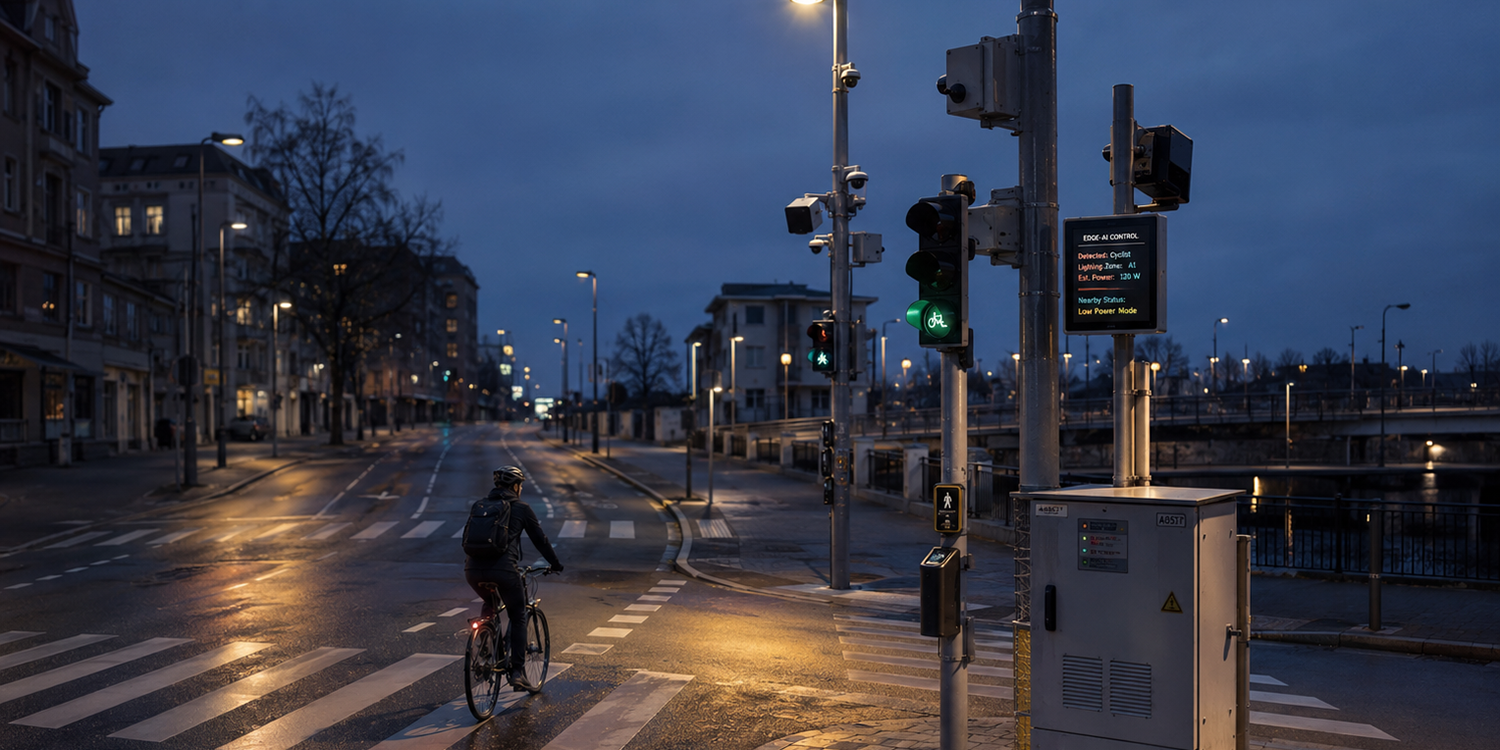
That matters because edge AI often operates close to real-world decisions. A cloud chatbot can be corrected after a bad response; an AI-powered industrial controller, vehicle component, or access-control device may act instantly. The closer AI gets to the physical world, the more important it becomes to prove that it is accurate enough, secure enough, explainable enough, and supervised by the right people.
For years, edge intelligence was mostly discussed in terms of speed, privacy, bandwidth, and efficiency. Those benefits still matter. Running AI on or near a device can reduce latency, avoid sending every piece of data to the cloud, and keep systems working when connectivity is poor.
The EU AI Act adds another question: can the system be trusted in context? A device that identifies defects on a production line is different from one that helps screen job applicants or supports medical decisions. The same technical capability can carry very different responsibilities depending on how it is used.
For high-risk AI systems, the official requirements include risk management, data quality, logging, technical documentation, clear information for deployers, human oversight, robustness, cybersecurity, and accuracy. Rules for certain high-risk areas are set to apply from 2 December 2027, while rules for AI embedded in regulated physical products apply from 2 August 2028.
In practice, this pushes edge AI teams to build trust into the product lifecycle, not bolt it on at the end.
The future of edge intelligence will not be shaped only by faster chips or smaller models. It will also be shaped by design choices that make AI easier to test, explain, update, and control.
A practical edge AI strategy now needs to cover:
These are not just legal questions. They are product quality questions. A device that cannot explain its limits is harder to maintain. A model that cannot be monitored is harder to improve. A system without clear ownership becomes risky as soon as it leaves the lab.
Compliance matters at the edge because many edge systems are distributed, embedded, and difficult to inspect after deployment. A cloud service can often be patched centrally; a fleet of connected devices may be scattered across hospitals, homes, factories, farms, stores, or city infrastructure. That makes documentation, monitoring, version control, and update procedures much more important.
The Act also affects companies outside the EU if their AI systems or general-purpose AI models are placed on the EU market or used in ways covered by the regulation. General-purpose AI obligations began applying on 2 August 2025, including duties around technical documentation, copyright policy, and summaries of training content, with extra obligations for models that present systemic risk.
For edge intelligence, this creates a ripple effect. A small device maker may depend on a model from a larger provider. A retailer may deploy devices from a vendor. A hospital may use equipment that includes AI components from several suppliers. Everyone in the chain needs clearer information about what the system does, how it was built, and where responsibility sits.
Good ai governance is not a binder of policies that appears right before release. It is a set of working habits that helps teams make better choices throughout development and deployment.
A simple governance checklist for edge AI might include:
This kind of governance does not have to slow innovation. In many cases, it prevents expensive rework. Teams that know their risk category, evidence needs, and oversight model earlier can build with fewer surprises later.
One of the biggest shifts is cultural. Edge AI used to be marketed mostly as invisible intelligence: the device simply became “smart.” The EU AI Act pushes the market toward accountable intelligence: users, deployers, regulators, and affected people should have a clearer sense of when AI is involved and how risk is managed.
Transparency rules are especially relevant where people interact with AI systems or encounter AI-generated content. The Commission’s materials explain that people should be informed in situations such as chatbot interaction, and that certain AI-generated content must be identifiable or labelled.
For device makers, this may influence interface design, user notices, product documentation, procurement materials, and support processes. For buyers, it changes the questions they ask vendors. “Does it work?” is no longer enough. The better question is, “Can we safely explain, supervise, and maintain how it works?”
How the EU AI Act is shaping the future of edge intelligence comes down to one practical idea: AI at the edge must be useful, but it must also be governable. The most competitive products will not simply process data faster. They will be easier to trust, audit, secure, update, and explain.
For builders, that means designing compliance and oversight into the product from day one. For buyers, it means asking sharper questions before deployment. And for everyone working with edge AI, it means treating governance as part of innovation, not as the opposite of it.
Comments are closed